Electrum fixes vulnerability that could let malicious servers divert Bitcoin payments
Electrum has released version 4.8.3 to address a high-severity vulnerability affecting earlier versions of the Bitcoin wallet. The flaw involved malicious Electrum servers and the handling of newly broadcast, unconfirmed transactions.
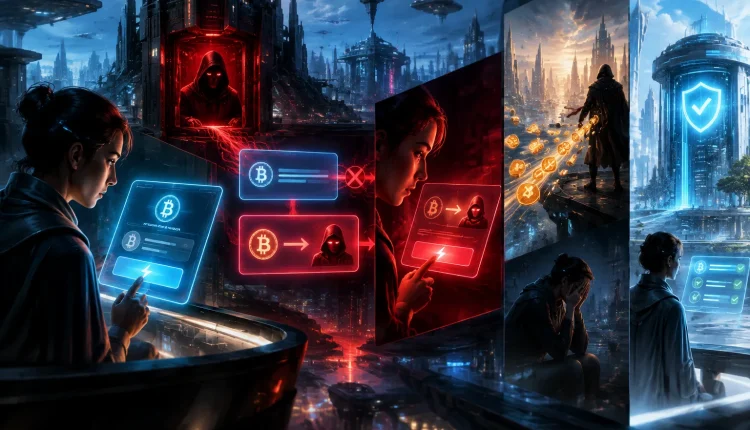
According to Electrum’s security advisory, an attacker operating a malicious server could suppress a user’s legitimate transaction and present a conflicting transaction that sent funds to an attacker-controlled address. The substituted transaction was invalid at that stage, but could be used in a later social-engineering step.
The risk emerged when a user attempted to speed up the displayed transaction using Replace-by-Fee, or RBF. In that scenario, the attacker could try to have the user sign the conflicting transaction, turning the earlier substitution into a loss of funds.
Online advertising service 1lx.online
Electrum said it received two reports related to the issue, including one report in which a user lost money after fee-bumping the substituted transaction. The wallet maker released the fix on October 24, 2026.
How the transaction substitution worked
The vulnerability applied to Electrum versions before 4.8.3 when a user relied on a malicious server. After a legitimate payment was broadcast but remained unconfirmed, the server could hide that payment from the wallet interface.
It could then show a conflicting transaction with an attacker-controlled recipient address. Electrum described that transaction as invalid before the user interaction, meaning the attack depended on persuading the user to take an additional step rather than automatically redirecting a completed payment.
If the user selected fee bumping through RBF, the attacker could attempt to get the user to authorize the substituted transaction. The incident illustrates why transaction details should be reviewed again when changing an unconfirmed payment, particularly where the recipient or outputs do not match the original intent.
- The attack targeted transactions that had been broadcast but were still unconfirmed.
- A malicious server could conceal the legitimate transaction from the user’s view.
- The final loss required the user to sign the conflicting transaction during fee bumping.
What changed in Electrum 4.8.3
Electrum 4.8.3 adds signature verification for relevant unconfirmed transactions, according to the advisory. That verification is intended to prevent the malicious-server substitution described in the disclosure.
The update is a wallet-side security fix rather than a change to the Bitcoin protocol. It follows continuing maintenance work across Bitcoin software, including the recent Bitcoin Core 31.1 release with chainstate and privacy fixes.
Online advertising service 1lx.online
Electrum said users who connected exclusively to trusted or self-operated Electrum servers were not exposed to this specific attack. The disclosure nevertheless underlines the security importance of the server a light wallet uses to obtain transaction information.
- Versions before 4.8.3 were affected.
- Version 4.8.3 was released on October 24, 2026.
- Trusted or self-operated servers were not affected by this specific attack.
Why fee-bumping deserves added scrutiny
RBF lets a user replace an unconfirmed transaction, commonly to increase its fee. In the reported attack path, that normal feature became the point at which a user could be asked to sign a different transaction from the one originally broadcast.
Electrum’s report does not indicate that every delayed transaction was at risk. The specific conditions included use of an affected wallet version, a malicious server and a later attempt to fee-bump the transaction. Still, the incident shows how wallet interface data and transaction signing prompts can become critical security controls.
Online advertising service 1lx.online
Users of affected versions can reduce exposure to this disclosed issue by moving to the patched release and by verifying transaction recipients and amounts before authorizing a replacement transaction.
- RBF is designed to replace an unconfirmed transaction, often with a higher fee.
- A replacement-transaction prompt should be checked independently of the original payment.
- The disclosed conditions required a malicious server connection and user authorization of the replacement.
Continue reading: Bitcoin Core 31.1 release with chainstate and privacy fixes on BTCNews.
Continue reading: Coinbase Ireland safeguarding settlement on BTCNews.
Sources
- Electrum / GitHub: Malicious server can replace a just-broadcast tx and try to trick user into RBF-ing it
- CoinDesk: Bitcoin wallet bug let rogue servers steal funds when users tried to speed up payments
Our creator. Creates amazing NFT collections! Support the editor - Bitcoin_Man(TON) / Bitcoin Man Stickers(TON) / BM Numbers (TON) / Comics Book (TON) / Bitcoin_Man (ETH)
Pi Network (Guide)is a new digital currency developed by Stanford PhDs with over 55 million participants worldwide. To get your Pi, follow this link https://minepi.com/Tsybko and use my username (Tsybko) as the invite code.
Binance: Use this link to sign up and get $100 free and 10% off your first months Binance Futures fees (Terms and Conditions).
Bitget: Use this link Use the Rewards Center and win up to 5027 USDT!(Review)
Bybit: Use this link (all possible discounts on commissions and bonuses up to $30,030 included) If you register through the application, then at the time of registration simply enter in the reference: WB8XZ4 - (manual)